Manager
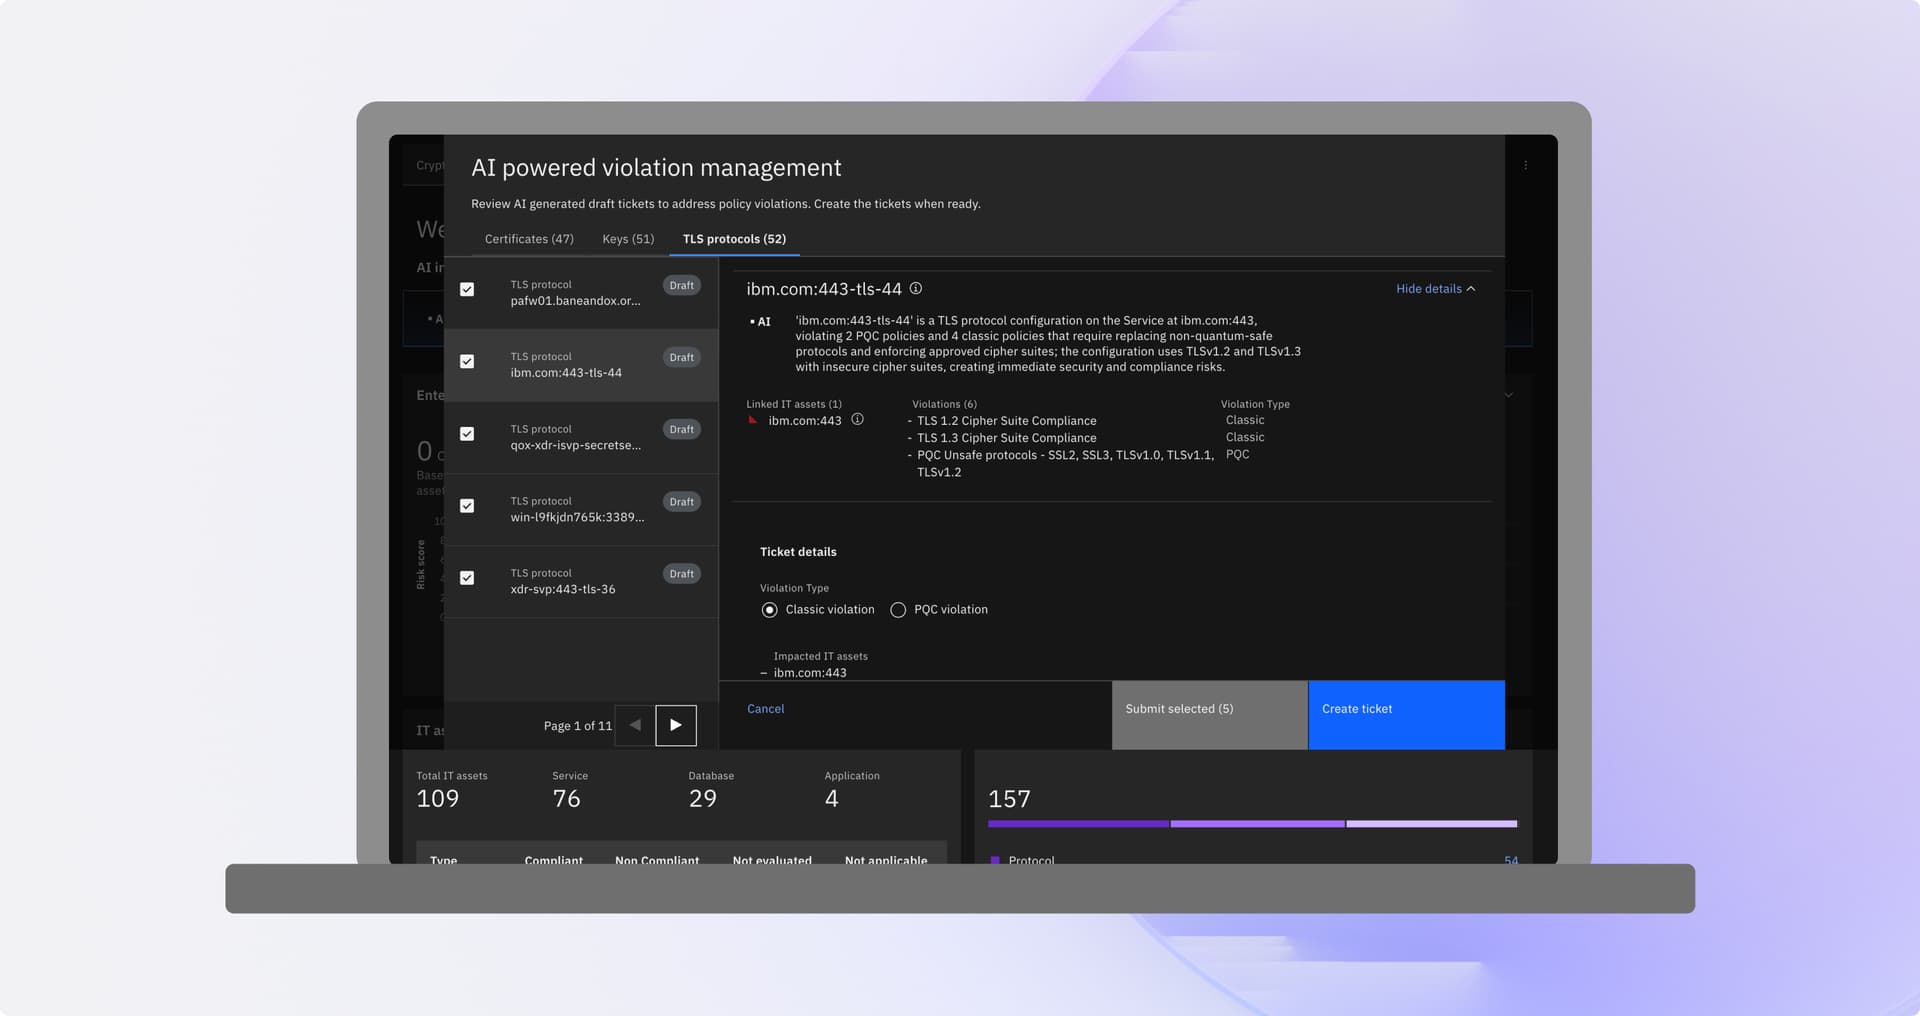
IBM Quantum Safe Cryptography Manager
A centralized inventory of cryptographic objects, mapped to the applications and infrastructure that depend on them, with risk and compliance posture in one view.
Read more
Crypto-agility starts with visibility. We work with IBM's Quantum Safe portfolio to discover where cryptography lives, assess the risk and move to post-quantum algorithms without breaking what works today.
Each tool covers a different layer: the enterprise inventory, the application source code, and the network traffic between clients and servers.
A centralized inventory of cryptographic objects, mapped to the applications and infrastructure that depend on them, with risk and compliance posture in one view.
Read moreScans application source code for cryptographic artifacts, vulnerabilities and crypto-agility anti-patterns, and produces a Cryptography Bill of Materials.
Read moreAn adaptive proxy that lets legacy and post-quantum-ready clients and servers talk to each other, without changing application code.
Read moreCryptography Manager builds a centralized inventory of cryptographic objects and their metadata: type, subtype, location and more. It maps dependencies between logical assets such as applications, software and databases, and physical assets such as servers, storage and networking devices.
On top of that inventory it evaluates your cryptographic posture, assesses risk and aligns your compliance posture against global standards such as NIST, GDPR and PCI-DSS.
Opens IBM's registration page. We can help you set up the trial and interpret the results.
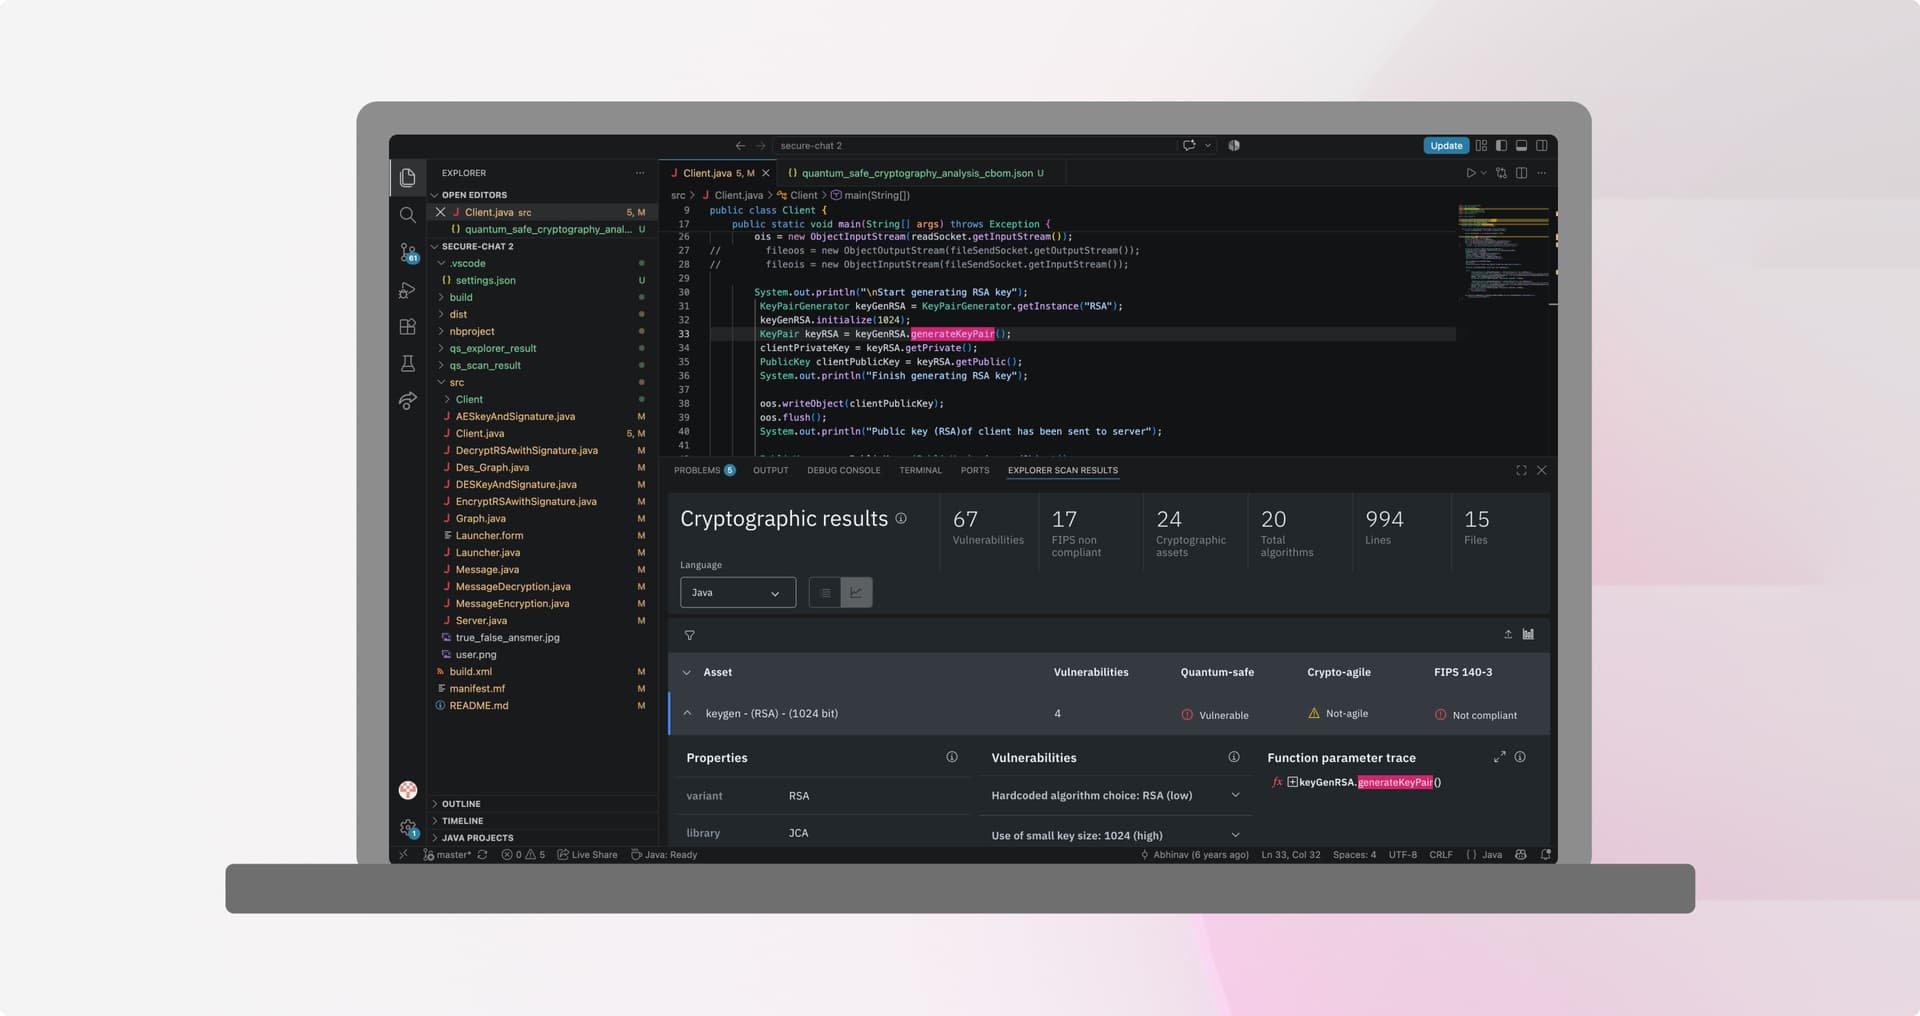
QSE discovers cryptographic artifacts, vulnerabilities and crypto-agility anti-patterns in source code, and uses those insights to guide code updates.
Scans are automated and integrated in the application's CI/CD build pipeline, so they become part of regular DevSecOps routines with near-zero manual effort. For every repository scanned, QSE generates a Cryptography Bill of Materials (CBOM).
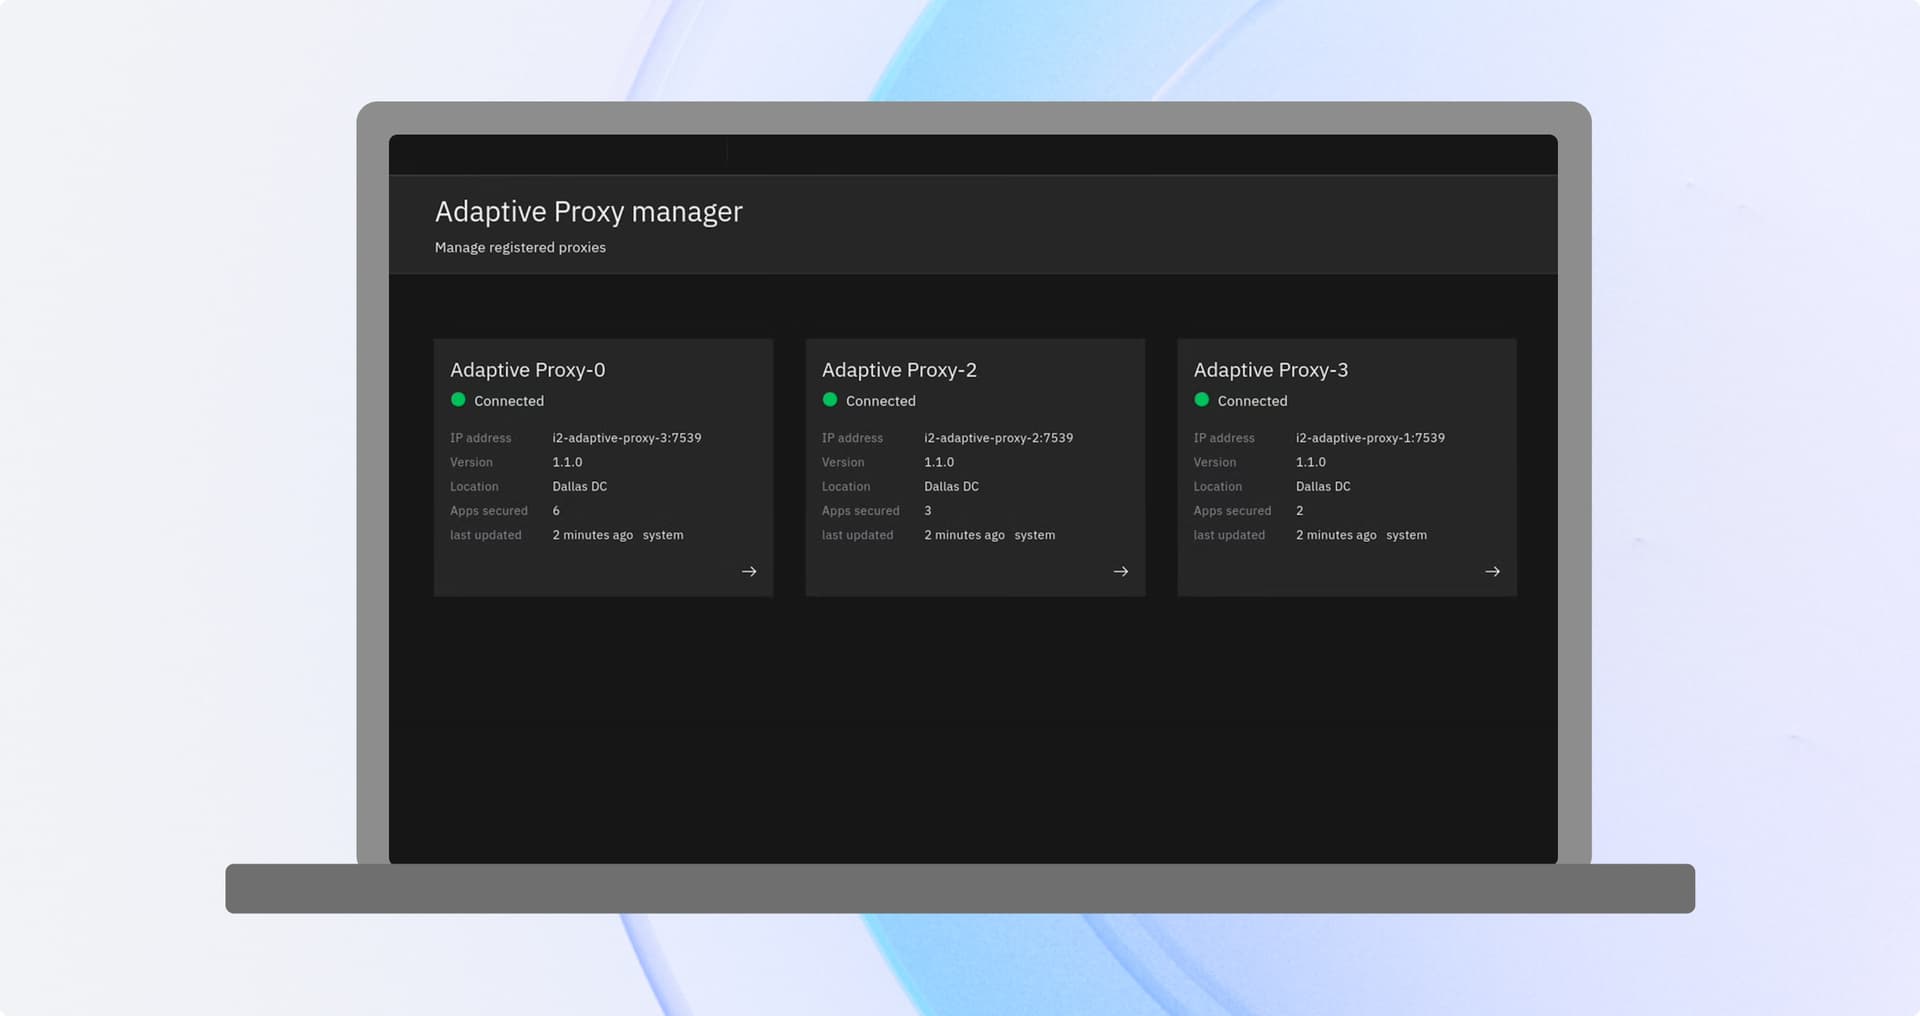
Quantum Safe Proxy is an adaptive proxy and performance test harness. It handles both legacy and post-quantum-ready clients and servers, enabling backward compatibility and interoperability without changing application code.
That makes it possible to protect traffic against "harvest now, decrypt later" while applications are still being migrated.
Source: NIST, August 2024
Tools do not make you quantum-safe on their own. We put them to work inside a structured approach.
Cryptography Manager and Quantum Safe Explorer build the cryptographic inventory and CBOM that every migration decision depends on.
Discovery serviceQuantum Safe Proxy protects traffic and bridges legacy and post-quantum systems while applications are migrated step by step.
Migration serviceCryptography Manager keeps the inventory, policies and key and certificate lifecycle under control long after the first migration.
Crypto-agility serviceWe specialise in IBM Quantum Safe, and we also know the alternative tooling in the market, so recommendations start from your environment rather than a product list.